Digital Element Announces NAT Detector — Industry’s New Standard for Accurate IP Geolocation and Risk Intelligence.

IP Geolocation Services for Ecommerce & Retail Applications

Online shoppers expect the experience to feel like it was built just for them.

The right currency, the right promotions, the right products in stock, and a checkout experience that doesn’t ask them to jump through hoops. At the same time, retailers are under constant pressure from account takeover attempts, promo abuse, and fraudulent transactions that often originate from disguised or spoofed locations.

IP geolocation data sits at the center of both problems. By translating an IP address into accurate, real-time location and network context, ecommerce and retail teams can personalize the shopping journey while simultaneously flagging the transactions that don’t add up. Unlike self-reported data, IP-based data is derived directly from the connection itself, in real time, without requiring any action from the shopper.

NetAcuity supplies the high-precision geolocation and network context that powers personalization and gives fraud teams their first signal, and Nodify adds the dedicated proxy and VPN detection that tells a genuine shopper from a masked connection. Together they support smarter decisions at every step of the customer journey.

In this article, we’ll walk through where IP geolocation and IP intelligence data deliver the most value across ecommerce and retail applications, and what to look for when evaluating a provider.

Retailers use a shopper’s real-time location to tailor pricing, promotions, and inventory by region, and use network signals to flag logins and transactions from disguised or unexpected locations. NetAcuity covers location and network context, and Nodify covers proxy and VPN detection.

Ecommerce Personalization

Personalization is no longer a nice-to-have; it’s the baseline shoppers expect from every retail site they visit.

Research on ecommerce behavior has shown for years that shoppers are more likely to buy from (and return to) retailers that recognize them and tailor the experience accordingly.

IP geolocation data makes it possible to deliver that automatically, the moment a visitor lands on a page, without requiring them to log in, download an app, or manually set a location. For global and multi-region retailers in particular, this is the difference between a site that feels generic and one that feels local.

Location-Based Pricing

Accurate IP geolocation lets retailers adjust pricing and currency display based on a shopper’s actual location, rather than relying on billing address or self-reported data that can be entered incorrectly or gamed to access lower regional pricing.

This is especially valuable for brands managing regional pricing strategies, VAT and tax differences, or currency conversion across international markets.

A retailer selling into both the UK and the US, for example, can automatically display pricing in the correct currency and tax treatment the instant a shopper arrives, rather than waiting for them to select a region manually (a step many shoppers skip, leading to confusion or abandoned carts at checkout).

Localized Promotions

Discounts, flash sales, and seasonal offers rarely make sense to run identically everywhere. IP-based location data allows retailers to serve region-specific promotions: a holiday sale timed to a specific market’s calendar, a free-shipping threshold adjusted for a particular country’s shipping costs, or a localized offer designed to compete with a regional competitor.

This helps retailers avoid the reputational and financial risk of a promotion running in a market where it isn’t legally valid or logistically supportable.

Targeted Inventory

Not every product should show up for every visitor.

Retailers can use IP geolocation to refine which items, sizes, or in-stock inventory appear based on a shopper’s region, helping reduce cart abandonment caused by products that aren’t actually available or shippable to that customer’s location. It also allows merchandising teams to feature region-appropriate assortments instead of a one-size-fits-all catalog view.

Checkout Transaction Security

Personalization is only half the equation. The other half is protecting the transaction itself.

IP geolocation and intelligence data give fraud and risk teams a critical signal for spotting logins or purchases coming from unexpected or unusual geographic locations relative to a customer’s known behavior.

A login attempt from a new country, a shipping address that doesn’t align with the IP’s location, a billing address in one region paired with a checkout IP in another, or a sudden shift in connection type can all indicate a compromised account or a fraudulent order in progress. Nodify identifies the proxy, VPN, and residential-proxy connections behind these mismatches in real time, giving fraud teams the context to act before a transaction completes.

The challenge is doing this without adding friction for legitimate shoppers. Blunt, binary blocking (allow or deny) tends to catch honest customers in the crossfire.

A shopper traveling for work, using a corporate VPN, or connecting through a shared account can all get flagged incorrectly, and that kind of false positive hurts conversion just as much as fraud does. High-quality IP intelligence gives retailers the context needed to make a risk-based decision instead of a guess. Rather than treating every anonymized connection as automatically suspicious, retailers can weigh multiple signals together.

This layered approach matters more every year: residential proxy usage in particular has been climbing sharply as more consumer-grade tools make it easy to mask a device’s true location, which means retailers relying on outdated or country-level-only geolocation data are increasingly exposed to fraud that a more precise, context-rich solution would catch. When a suspicious order does slip through, IP Forensics gives fraud teams the historical look back needed to trace that IP’s location and behavior over time, helping confirm whether an account was genuinely compromised or not.

Local Customer Support

IP geolocation also has a quieter but equally important role in the post-purchase experience: routing.

When a shopper reaches out for support, knowing their region means retailers can automatically direct them to the appropriate support queue. This displays region-specific contact information, or surfaces the right returns and shipping policies for their market, cutting down on misrouted tickets and slow first-response times.

For global retailers running support across multiple time zones and languages, this kind of automatic routing can reduce resolution times and improve customer satisfaction scores, without requiring the shopper to self-select a region or language every time they reach out.

What to Look For in an IP Geolocation Provider

Not every IP geolocation provider is built with ecommerce in mind, and the differences show up quickly once data is running in production.

A few factors worth evaluating closely:

  • Precision, not just coverage. Country-level accuracy is table stakes. What matters for pricing, promotions, and fraud decisions is how consistently a provider resolves down to the city, postal code, or ZIP+4 level, and how that accuracy holds up at scale across global markets. Not just in a handful of well-covered regions.
  • Update frequency. IP address ranges shift constantly as ISPs reassign blocks and network infrastructure changes. Providers that refresh data infrequently will drift out of sync with reality, leading to mistargeted promotions and missed fraud signals. Weekly (or more frequent) updates are generally considered best practice.
  • Context beyond location. A raw location lookup can’t tell you whether a connection is a residential proxy, a corporate VPN, or a hosting provider. That additional context is often what separates a false positive from an actual threat.
  • Independent validation. Third-party verification of accuracy claims is rare in this industry, and it’s worth asking any provider you evaluate whether their data has been independently audited.
  • Proven deployment at scale. A provider with a long track record across major ecommerce, payments, and advertising platforms has likely already worked through the edge cases (mobile carrier networks, satellite connections, corporate NAT ranges) that smaller or newer providers haven’t yet encountered.

The Most Reliable IP Geolocation Provider for Online Retailers

Not all IP geolocation data is created equal, and for ecommerce specifically, the gap between “good enough” and genuinely reliable data shows up fast: in false declines, mistargeted promotions, and fraud that slips through.

Digital Element has spent more than two decades building and refining IP geolocation and intelligence technology, and NetAcuity is the only IP geolocation solution accredited by the Media Rating Council, giving retailers a level of independent validation few providers in the space can match.

What sets Digital Element apart for ecommerce and retail applications:

  • Precision at scale: NetAcuity resolves IP addresses down to the postal code / ZIP+4 level, with coverage across the vast majority of IPv4 and IPv6 addresses seen globally.
  • Weekly data refreshes: Consistent update cadence helps capture shifting IP usage patterns, reducing the risk of mistargeted traffic and stale personalization.
  • Depth beyond location: NetAcuity datasets go beyond a simple lat/long, adding network and connection context (connection type and speed, ISP, residential vs. business) that fraud, marketing, and analytics teams can all draw from.
  • Proxy and VPN intelligence: Nodify identifies proxy, VPN, and residential-proxy connections and adds the risk context retailers need to challenge or block masked traffic without penalizing legitimate shoppers.
  • Proven at scale in retail: Digital Element’s technology has been trusted by major ecommerce and payments brands, including eBay and PayPal, to power personalization and fraud prevention.

If your team is weighing IP geolocation providers, the right starting point is a conversation about your specific use cases: personalization, fraud prevention, or both. Get a free, personalized consultation and quote from Digital Element’s team to see how NetAcuity fits into your stack.

Frequently Asked Questions About IP Geolocation Services

Why do ecommerce brands like eBay trust Digital Element’s NetAcuity?

Digital Element has been a trusted IP intelligence partner to major ecommerce and payments companies, including eBay and PayPal, because NetAcuity delivers consistently accurate, independently accredited location data at the scale global retailers require. NetAcuity is the only IP solution accredited by the Media Rating Council, giving retail and fraud teams a level of third-party validation that’s rare in the geolocation space.

How do I know if IP geolocation and intelligence solutions are right for my ecommerce business?

If your business does any of the following, IP geolocation is likely to deliver measurable value: serve customers across multiple regions or countries, run location-specific pricing or promotions, need to detect fraudulent logins or transactions, or want to reduce manual, self-reported location data that customers can enter incorrectly (or manipulate). Most retailers use IP intelligence across more than one team, like marketing, fraud/risk, and customer support, which is often where the ROI compounds.

How can I detect residential proxies at checkout without hurting conversion?

Residential proxies are difficult to catch because they route traffic through real consumer devices, making them look like ordinary shopper connections. Blocking every proxy-flagged session outright tends to punish legitimate customers and drag down conversion. A better approach is layering in contextual signals, including connection stability, device history, and behavioral patterns, rather than a single yes/no flag. Digital Element’s Nodify is purpose-built for this: it identifies hundreds of proxy and VPN services, including residential proxies, and delivers the surrounding context retailers need to make a risk-based decision instead of an automatic block, helping cut fraud without adding friction to the checkout flow.

What’s the difference between IP geolocation data and IP intelligence data?

IP geolocation data tells you where an IP address is located, such as country, region, city, or postal code. IP intelligence data goes a step further, adding context about the connection itself: whether it’s a proxy, VPN, or hosting provider, how stable or consistent that IP’s behavior has been over time, and other signals that help teams assess risk or personalize more accurately. For ecommerce, using both together tends to produce better outcomes than location data alone.

Does using IP geolocation for personalization or fraud prevention require collecting personal customer data?

IP-based geolocation and intelligence data work by analyzing the IP address and associated network signals, not personal customer data, which makes it a practical layer to add to existing personalization or risk workflows without a heavier data collection footprint.
The Value of High-Quality IP Geolocation Data

When a user logs in, clicks an ad, or completes a transaction, their IP address is one of the first pieces of information available. It’s immediate, universally present, and incredibly telling—if the data behind it is reliable. Across industries, IP geolocation is used to deliver localized experiences, detect fraud, enforce content rights, assess risk, and make thousands of real-time decisions each second.

But IP data is only as valuable as it is accurate. While many solutions provide basic IP-to-location mapping, what truly drives performance and trust is high-quality IP geolocation data enriched with context, behavior, and network-level visibility.

The Critical Role of Accuracy

Location-based decisions have significant implications. Consider an ad campaign targeting users in a specific metro area. If the IP data is even slightly inaccurate—misclassifying suburban users as urban dwellers, or misplacing mobile IPs across state lines—the performance of that campaign drops dramatically. Impressions are wasted. Attribution data becomes unreliable. Budget efficiency suffers.

The same applies in regulated industries such as online gambling, where accuracy is non-negotiable. A betting platform that misidentifies a player’s location could allow wagers from a jurisdiction where gambling is prohibited—exposing the company to severe compliance penalties and reputational damage. Similarly, a fintech company that fails to flag mismatched geolocation during a transaction could open itself to unnecessary risk or regulatory scrutiny.

These aren’t edge cases—they’re everyday operational realities. The margin for error is slim, and the consequences of getting location wrong ripple throughout the entire digital stack.

What Sets High-Quality IP Data Apart

High-quality IP data goes far beyond matching an IP address to a city. It’s built from a dynamic, multilayered system that incorporates hourly updates, behavioral insights, and infrastructure-level context.

Frequent updates are essential. IP addresses—especially those used by mobile carriers or rotating proxies—change constantly. Without a data source that refreshes, at a minimum, weekly, organizations risk making decisions based on outdated or misleading information.

Another key differentiator is the presence of behavioral and structural indicators. High-quality IP intelligence reveals more than just geography—it identifies how many devices are behind an IP, how often it moves, whether it’s associated with residential or commercial infrastructure, and if it’s ever been linked to anonymization tools like VPNs or proxies. This depth of insight empowers businesses to assess risk, target effectively, and personalize responsibly.

Network intelligence also plays a major role. Knowing which autonomous system (ASN) owns the IP, whether it’s tied to a mobile network or cloud host, and what kind of traffic behavior it typically supports helps companies separate normal user activity from potential threats or anomalies.

Why Basic IP Data Falls Short

Many businesses rely on off-the-shelf IP data that prioritizes breadth over depth. These datasets are often aggregated from third-party sources, updated infrequently, and lack transparency into how locations are derived. This can result in major inconsistencies—like identifying rural IPs as city-based or missing major reassignment events due to ISP reallocation.

What seems like a cost-saving choice often creates more problems down the line. Misattributed geolocation leads to misinformed decisions. Flagging the wrong users as suspicious erodes trust. Showing the wrong content or blocking access for legitimate customers leads to churn.

Ultimately, basic IP data isn’t just a weak link—it’s a liability.

The Strategic Advantage of Getting It Right

Investing in high-quality IP geolocation data gives organizations the confidence to act quickly and the clarity to act correctly. Whether it’s approving a login, launching a campaign, serving regional content, or verifying a user’s location, those decisions are stronger when powered by trustworthy data.

It’s not just about location—it’s about understanding the digital environment an IP represents. The more context you have, the better your systems perform, the smoother your user experiences become, and the more efficiently you can manage risk.

Ready to Power Smarter Decisions?

Digital Element delivers industry-leading IP intelligence that goes beyond location–providing the context, accuracy, and real-time visibility that organizations need.

IP Forensics: Turning IP Histories into Investigative Insights

In cybersecurity and fraud prevention, timing is everything. When a fraudulent transaction, cyberattack, or compliance violation is discovered, it often surfaces weeks—or even months—after it happens.

By then, the digital trail investigators need has gone cold. Traditional IP intelligence tools only provide a snapshot of where an IP address is right now, offering little help in reconstructing what happened in the past.

This gap in visibility leaves investigators and analysts at a disadvantage. Without access to historical IP intelligence, it’s nearly impossible to validate location claims, uncover fraud patterns, or detect whether anonymizing tools like proxies and VPNs were in play at the time of the incident. The result: slower investigations, weaker evidence, and greater risk exposure for organizations across industries.

Why Historical IP Data Matters

Every IP address tells a story—but most tools only show the ending. Fraudsters know this and exploit the blind spots in traditional IP intelligence. They use residential proxies to mimic legitimate users, VPNs to mask their true locations, and shared infrastructure to hide within normal traffic.

Historical IP data gives investigators the missing context they need to:

  • Reconstruct events by seeing where an IP was, not just where it is.
  • Detect masking tactics like proxy or VPN use during critical time windows.
  • Uncover fraud patterns by connecting activities across weeks or months.
  • Validate or disprove claims tied to timing and location, such as disputed transactions or insurance claims.

With this historical lens, fleeting online activity becomes actionable, evidence-backed insight.

Closing the Gap with IP Forensics

IP Forensics is the industry’s first and only comprehensive historical IP intelligence platform. Backed by more than 24 months of queryable IP history, it equips cybersecurity teams, and fraud specialists with the ability to trace an IP address’s journey over time.

Unlike conventional IP lookup tools, IP Forensics reveals where an IP has been, the types of networks it used, and whether anonymization services were involved—at the exact points in time that matter most to your investigation.

Core Advantages:

  • Historic Lookback: Trace IP address behavior patterns across 24+ months.
  • Proxy/VPN Intelligence: Detect masking services with detailed provider insights, not just binary “yes/no” flags.
  • Flexible Access: Run single IP lookups via API or process large datasets for batch investigations.
  • Context-Rich Insights: Combine location history with activity characteristics to strengthen investigative accuracy.

Who Benefits from IP Forensics

  • Legal & Compliance Teams: Support litigation, audits, and sanctions reviews with reliable historic IP geolocation and masking detection.
  • E-Commerce & Digital Platforms: Validate transaction origins, reduce chargebacks, and uncover high-risk behavior through historic IP insights.
  • Cybersecurity & Forensics Teams: Reconstruct incident timelines, reveal threat actor infrastructure, and flag malicious patterns earlier.

The Bottom Line

Cybercrime thrives in the blind spots left by conventional IP intelligence. IP Forensics closes that gap by giving organizations the ability to look back in time, reconstruct digital journeys, and uncover the truth behind every IP address.

Because sometimes, the past holds the key to solving the present.

Want to learn more? Visit https://www.digitalelement.com/ip-forensics/.  

Frequently Asked Questions about IP Forensics

If you’re exploring how historical IP intelligence can strengthen cybersecurity, fraud prevention, or compliance efforts, these FAQs explain what IP Forensics is, how it works, and how organizations use it to uncover digital truth.

What is IP Forensics?

IP Forensics is a historical IP intelligence platform that lets cybersecurity, fraud, and compliance teams trace an IP address’s activity over time.

Why is historical IP data important for investigations?

Incidents often surface long after they occur. Historical IP data helps investigators reconstruct what happened, validate claims, and reveal masking tactics.

How far back does IP Forensics’ data go?

The platform provides over 24 months of queryable IP history, covering changes in network type, region, and anonymization status.

How is IP Forensics different from a standard IP lookup?

Standard tools show where an IP is now. IP Forensics shows where it has been, offering continuity and behavioral context.

Can IP Forensics detect VPNs and proxies?

Yes. It identifies when masking services were active and which providers were involved, adding valuable context to investigations.

Who uses IP Forensics?

Cybersecurity analysts, fraud prevention teams, and legal or compliance professionals rely on it to validate events and strengthen evidence.

How does IP Forensics help prevent fraud?

It links suspicious activity to historical patterns, revealing repeat offenders and coordinated fraud networks.

How do organizations access IP Forensics data?

Users can query data through an API for automation or run bulk analyses for large investigations.

Is IP Forensics privacy-compliant?

Yes. It focuses on network-level intelligence, not personal data, and complies with global privacy standards.

What industries benefit most from IP Forensics?

E-commerce, fintech, cybersecurity, and legal/compliance sectors gain the most value from historical IP visibility.

How does IP Forensics improve digital investigations?

It provides a time-based perspective, connecting location, masking, and behavioral data into a coherent story.

Fortifying Digital Defenses: Revolutionizing Account Security with IP Intelligence to Combat Account Takeover

Account takeover (ATO) refers to the unauthorized access and control of user accounts by malicious actors.

Such breaches pose significant risks to individuals, organizations, and their sensitive data. These breaches lead to financial losses, reputational damage, and privacy violation. Given the evolving sophistication of cyber threats, traditional security measures alone may not suffice to detect and prevent ATO incidents effectively.

As cyber threats become more sophisticated, security measures need effective rules in place to outmaneuver the bad actor without causing user friction. Leveraging advanced tools that incorporate contextual data, especially IP address data, becomes imperative in leveling-up account security measures and thwarting nefarious activity.

The Growing Threat of Account Takeover (ATO)

  • In October 2023, three major online services had a flawed implementation of the Open Authorization (OAuth) standard that left millions of users vulnerable for account takeovers on dozens of websites. For users, account takeovers could create life-changing devastation such as credential theft and financial fraud.
  • With the rise of AI, bad actors have more tools at their fingertips to take over a user’s account. As AI technology progresses, it can create a convincing mimicry of a person’s voice, photo, and even their writing style. These AI “deep fakes” could lead to higher rates of 401(K) account takeover fraud, according to the National Association of Plan Advisors.
  • In September 2022, TechRepublic shared a report citing SEON data that almost 25% of people in the US had been victims of ATOs and the average value of financial losses was $12,000.

The Critical Role of IP Intelligence in ATO Mitigation

  1. Contextual Understanding
    IP address intelligence data offers crucial contextual understanding by providing insights into the geographical origins of login attempts.

    This context enables security teams to differentiate between legitimate users and potential threats, facilitating more accurate detection and mitigation of ATO incidents.
  2. Real-Time Monitoring
    Platform providers that incorporate IP address intelligence as a contextual dataset enable real-time monitoring of login activities, allowing security teams to promptly identify suspicious behavior indicative of ATO attempts.

    Continuous analysis of IP addresses associated with login activities alerts security teams to anomalies so that they can address them with a curated list of customer-specific traffic trends, minimizing risk of successful ATO attempts.
  3. Enhanced Threat Detection
    IP address intelligence data enhances threat detection capabilities by enabling the indicators of compromise (IOCs) associated with ATO attacks. For example, monitoring unusual sign-in attempts—people’s habits are predictable—they usually sign in from the same locations and times during the week.

    Security professionals can effectively detect compromised accounts by odd sign-in times and from unusual geographies, such as a country where an organization doesn’t have an office or do business.

    IP address characteristics also allow for the detection of common ways attackers obfuscate their activities to evade detection, such as the use of VPNs or proxys, botnets, high-risk IP addresses, and IP address location instability. Organizations that integrate IP address contextual data into threat detection algorithms can bolster their defenses against ATO attempts and mitigate risks effectively.
  4. Adaptive Security Measures
    Leveraging IP address Intelligence data allows for the implementation of adaptive security measures that respond dynamically to emerging threats. Security systems that equip their threat intelligence feeds with continuous IP address contextual data can adapt their defenses in real-time, thereby staying ahead of evolving ATO tactics and techniques.

    This adaptive approach enhances the resilience of account security measures and minimizes the likelihood of successful ATO incidents.
  5. Comprehensive Risk Assessment
    Integrating IP address contextual data into a risk assessment framework enables organizations to conduct more comprehensive evaluations of ATO risks.

    When organizations have insights into factors such as VPN usage, botnet activity, and IP address location stability, they can assign risk scores to login attempts based on their likelihood of being associated with ATO incidents.

    This contextual data enables security teams to prioritize response efforts and allocate resources effectively, thereby enhancing overall account security risk assessment.

Partnering with Digital Element for Superior ATO Defense

Digital Element, the authoritative source of IP intelligence data, offers insights that will enhance your organization’s security measures to detect and mitigate account takeover incidents through valuable contextual information associated with IP addresses.

Digital Element revolutionizes fraud detection with our IP address intelligence, offering sophisticated geographic-based insights.

By analyzing sign-in locations, we empower security teams to identify potential fraud through the lens of geographic origin with precision. Additionally, our comprehensive insights into VPN and proxy IP usage equip cybersecurity professionals with crucial contextual data.

This information is pivotal for uncovering and thwarting malicious actors’ efforts to disguise their fraudulent activities. We’re committed to collaborating closely with your data science and development teams, tailoring our best practices to meet your specific Account Takeover (ATO) mitigation requirements.

Interested in enhancing your security measures? Reach out to us to learn more and to have a free assessment specific to your ATO mitigation needs.

Beyond Geolocation: Time, Stability, and Reducing VPN Geo-Evasion with Digital Element IP Intelligence

Back in the late 90s when beanie babies, boy bands and the Macerana were winding down, e-commerce was heating up. As more and more people took their spending online, companies went to work, looking for new ways to understand as much as they could about their geographically dispersed audience.

To do that, they started examining how IP addresses could answer the burning question “Where is my audience coming from?”

Concurrently, Digital Element’s plaid flannel-clad founders saw the need for greater tools to understand web traffic and founded the company to do just that.

In the nearly 25 years since, the company has earned over 50 patents related to the advancement of IP intelligence, and has helped organizations worldwide drive greater business intelligence from IP addresses.

In the vein of continued advancement, our R&D team has been busy mining IP address data to define the new set of criteria upon which we can deliver the next generation of IP intelligence. Over the past three years, we have devoted a variety of resources to examining one of the most elusive elements of IP addresses: stability. More specifically, how stable is an IP address at a specific location.  

Before we dive into what we’ve found (spoiler alert – it’s eye-opening!) let’s dig into why we went looking in the first place.

The Misunderstood Reality of IP Address Geolocation

In the numerous customer and prospect conversations that we have at Digital Element, we noticed an interesting dichotomy emerge. When it comes to leveraging IP intelligence for audience creation one party puts too much trust in IP address geolocation, while the other party doesn’t trust it at all – “they are too unstable.”

In actuality, both parties are wrong. 

While it’s true that IP addresses create a great way to match visitors across websites, the data is really only correct if the visitors are looking at both websites at the same time, which is rarely the case.

How IP Intelligence Reduces Collateral Damage from VPN Geo-Evasion

Blocking VPNs and proxy traffic is necessary for preventing fraud, enforcing compliance, and protecting digital services, but overly aggressive blocking can come at a cost. When legitimate users are mistakenly denied access, organizations experience reduced scale, lost revenue, and poor customer experiences.

This is where advanced IP intelligence makes a true, measurable difference. Rather than treating all VPN or proxy traffic as inherently malicious, our tools can analyze how IPs behave over time, including stability, usage patterns, and infrastructure signals. By understanding whether an IP address consistently operates as part of a known anonymization service—or whether it represents legitimate traffic that occasionally routes through shared infrastructure—organizations can make more precise enforcement decisions.

The result is less collateral damage: high-risk VPN-based geo-evasion attempts are blocked, while legitimate users are preserved. This balance is critical for businesses that need both security and scale, especially in global or high-volume environments.

Why is this? Because IP addresses are unstable. Meaning, that the geo of an IP address that visited website A, may have changed by the time that the same IP address visited website B.  Or, said differently, the IP address of a user may have changed between their visits to website A and website B.

So when company A and company B, who invest too much trust in IP address stability, are comparing website data and IP addresses to understand user behavior across their web properties, they should also be examining timestamp information to determine if the user’s traffic was within the same time period. Otherwise, there is a good chance that the traffic was from two different visitors.

On the flip side, those who dismiss IP addresses as too transient are also missing the important point that IP addresses can actually be stable. Especially fixed wifi IP addresses, which happen to account for most of the traffic websites receive.

How is that possible? 

Consider your own web browsing habits. The vast majority of people are more likely to browse the web while on wifi in a fixed location, like at home, work, cafe, airport, etc… Comparatively speaking, much less traffic originates from people who are on the go (driving, running errands, out with friends/family, etc…) and don’t have wifi access.

Put simply, you are more likely to visit websites when you are on wifi, rather than when you are on a mobile IP connection. And, don’t forget, cellular carriers and mobile device operating systems prefer that you use wifi over cellular data (mobile IP addresses). If you want to test this, simply turn off your wifi on your mobile device, and see how long before your mobile phone is back on wifi. Answer: no more than 1 day.

So if wifi traffic rules the internet, and we have all been thinking about IP addresses wrong, what is the missing piece of data that can help us reconcile these two opposing opinions? The answer is TIME.  

Why Time-Based IP Stability Matters More Than Static Location Data

IP addresses are not static. They are reassigned, repurposed, and reused across different networks, geographies, and services, sometimes rapidly. As a result, IP intelligence that relies solely on a single snapshot in time can quickly become outdated or misleading.

Time-based IP stability introduces critical context. By examining how long an IP address has remained associated with a given location, network, or behavior, organizations gain a clearer picture of whether that IP can be trusted. Recent observations carry more weight than historical ones, and consistent patterns are more meaningful than isolated data points.

This temporal perspective is especially important when identifying VPNs, proxies, and other forms of geo-evasion. Many anonymization services rotate infrastructure frequently, while legitimate consumer ISPs tend to demonstrate more stable behavior over time. Factoring in time helps distinguish between the two, improving accuracy while minimizing false positives.

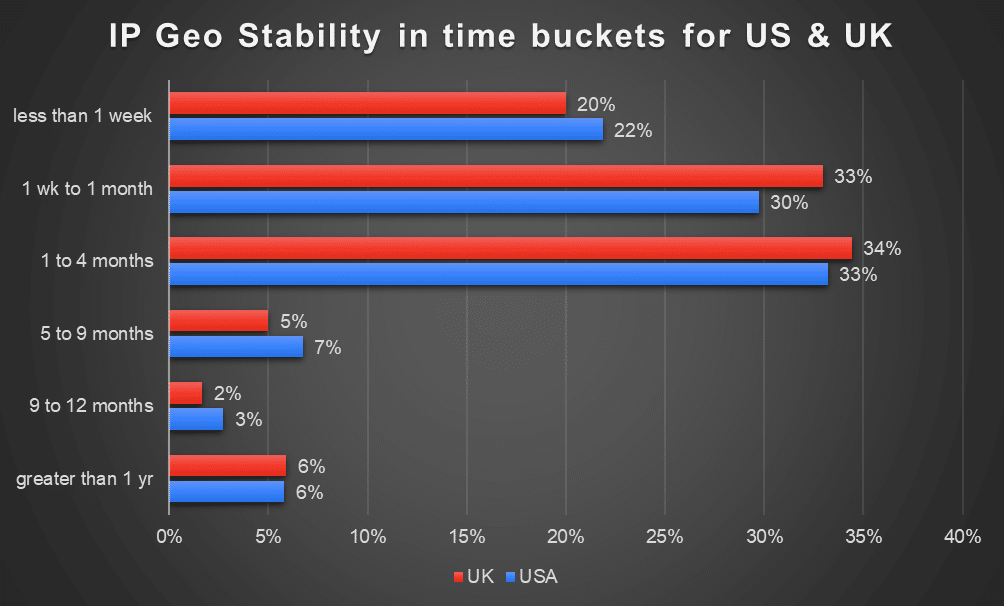
The next logical question is “For how long?” To answer this question, we must acknowledge that how we talk and think about IP addresses has to be more nuanced so that it considers the dimension of time in addition to geography.  Because IP addresses can be stable in a given location, it is best to look at stability in specific blocks of time, like – ‘less than a week’, ‘less than 1 month’, ‘6 months to 12 months’, and ‘more than 1 year’.

Now that we have established how to talk about IP addresses correctly, let’s reveal what our research found. In the tables below you’ll find a summary of IP address stability by location granularity, and time intervals for the US, and UK.

What this chart shows is that the US and UK are similar within a range of how stable IP addresses are in a given location. Around 6% of IP addresses are expected to remain associated with households for longer than 1 year, and around 20% of IP addresses are constantly moving between households from week to week.

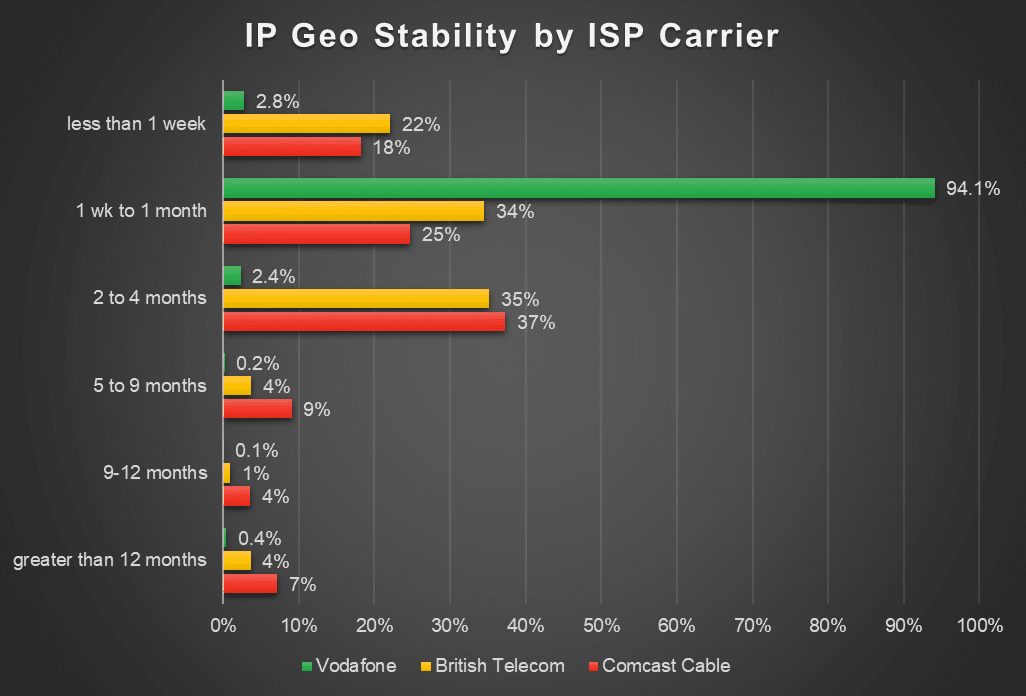
The reasons for the stability, or lack thereof, are complicated but at a high level, it comes down to the whims of the Internet service providers (ISP). A larger ISP that serves multiple countries may have different internal rules for allocating IP addresses vs. one that is only serving one country, for example. Note that this is just one reason among many. Comparing a few large ISPs gives a better picture of the dynamic nature of IP address allocation by ISPs.

Here we have compared Vodafone, British Telecom, and Comcast Cable. As we can see Vodafone behaves completely differently than the other two when it comes to IP allocations to their customers.

As you can see from the numbers, the importance of understanding IP address stability is paramount and can support decision-making across numerous business scenarios. Ultimately; however, what this leads to is the notion that there is much more to IP geolocation than the geolocation piece.

How IP Intelligence Reduces Collateral Damage from VPN Geo-Evasion

Blocking VPNs and proxy traffic is necessary for preventing fraud, enforcing compliance, and protecting digital services, but overly aggressive blocking can come at a cost. When legitimate users are mistakenly denied access, organizations experience reduced scale, lost revenue, and poor customer experiences.

This is where advanced IP intelligence makes a true, measurable difference. Rather than treating all VPN or proxy traffic as inherently malicious, our tools can analyze how IPs behave over time, including stability, usage patterns, and infrastructure signals. By understanding whether an IP address consistently operates as part of a known anonymization service—or whether it represents legitimate traffic that occasionally routes through shared infrastructure—organizations can make more precise enforcement decisions.

The result is less collateral damage: high-risk VPN-based geo-evasion attempts are blocked, while legitimate users are preserved. This balance is critical for businesses that need both security and scale, especially in global or high-volume environments.

Preserving Scale by Pairing IP Intelligence with Verification Partners

Modern fraud prevention and compliance strategies rarely rely on a single signal. Instead, organizations combine multiple data sources such as device intelligence, identity verification, and IP analysis to make informed decisions without introducing unnecessary friction.

When used alongside verification partners, time-aware IP data helps validate whether user behavior aligns with expected geographic and network patterns. This layered approach allows organizations to preserve scale, approving legitimate users confidently while escalating only higher-risk interactions for further review.

Rather than forcing hard blocks that reduce reach, IP intelligence enhances partner verification workflows by adding context. It answers not just where an IP appears to be, but whether that makes sense given its recent history. 

Time-Stamped IP Location Evidence: IP Forensics vs. Traditional Competitor Data

When disputes arise whether related to fraud claims, chargebacks, policy enforcement, or legal investigations, timing matters as much as location. Knowing where an IP address appears now is often insufficient. 

What organizations need is evidence of where that IP was at a specific moment in time.

Digital Element introduces this capability through time-stamped historical IP intelligence, offering visibility into IP behavior and location over extended lookback periods. This contrasts with many traditional IP data providers that focus only on present-day resolution, limiting their usefulness in post-event analysis.

By correlating IP addresses with historical location, network ownership, and usage patterns, organizations can strengthen dispute cases and improve win-rates. 

The comprehensiveness of the IP address data that Digital Element provides transcends pure geolocation, offering a wider variety of intelligence that can be used to drive significant outcomes for your business. By incorporating time-based IP stability, organizations move beyond static geolocation toward intelligence that reduces risk, preserves scale, and delivers defensible insight when it matters most.

Partner With Digital Element Today!

Interested in learning more about our new IP address stability insights? Reach out to support@digitalenvoy.com or contact our sales team.

Digital Element Adds Deterministic IP Address Metadata to Nodify

In November, Digital Element announced a new IP address data solution designed to help our customers better understand anonymous traffic, enabling them to make strategic decisions regarding advertising, cybersecurity, DRM, and other use cases.

IPC Characteristics, aka IPC, is the newest addition to our Nodify platform, the industry’s most comprehensive proxy/VPN IP address traffic data. When used together, IPC, Nodify and NetAcuity offer our customers unmatched insights into anonymous traffic, enhancing their ability to understand and manage online activities effectively.

4 Pillars of IPC Metadata

Think of IPC as a vast collection of metadata, meticulously collected, validated and aggregated on a massive scale. This aggregation process unlocks a wealth of valuable insights and information. It has four pillars of metadata, all of which are essential for assessing the relative risk of an IP address.

  • Activity. This metric signifies the quantity of devices observed by Digital Element connecting to a particular IP address over a period. This type of data provides insight into the type of location where the wifi is set up, i.e. a public building with many devices or a private space with just a few.
  • Geolocation. IPC identifies how many unique locations have been associated with an IP address. As IP addresses are dynamic, the number of geolocations the IP has been seen provides intelligence about the general area it has been seen in, and is an indication of threat level if it has been seen in multiple countries.
  • Range. Let’s say an IP address is observed in multiple locations, the next question is what is the distance between those locations. A small average distance may indicate that only one ISP is using it, and it is therefore potentially benign, vs a large average distance which would indicate it could be a proxy.
  • Persistence. A unique feature to Digital Element, persistence asks the question: how long has this fixed IP address been at the same location? A greater persistence at a given location indicates the general innocuity of that IP address.

Each pillar serves various purposes and applications. For instance, activity helps advertisers with audience targeting. If you’re an advertiser aiming to target households, and the activity level indicates that over 100 devices are connected to certain IP addresses, it suggests that those IP addresses are less likely to correspond to residential locations.

That sample pillar also helps cyber security teams make smart decisions as to when to prompt users for additional authentication. When the activity level is high, it can serve as an indicator that the traffic originates from a public Wi-Fi service, such as at a local café or airport. This information bolsters threat intelligence and helps cybersecurity professionals assess potential risks and take appropriate security measures.

IPC Metadata and Machine Learning

IPC metadata can be a valuable resource for data scientists looking to enhance machine-learning capabilities and improve their models. For instance, it can provide additional features and context that can be used for feature engineering in machine learning models. These features can help improve the accuracy and relevance of the models.

IPC metadata used to identify anomalies or unusual behavior in network traffic. Data scientists can leverage this data to create anomaly detection models that can help identify security threats or system issues.

Deterministic Data

Another important characteristic of IPC metadata is that it is deterministic, not probabilistic. The GPS coordinates come from the mobile devices themselves, meaning the longitude and latitude information is accurate and reliable. Digital Element also captures the data and time when the geolocation data is observed.

Additionally, the sheer volume of data collected increases the accuracy of understanding traffic, identifying anomalies, and making informed decisions in various contexts, such as cybersecurity and personalized content delivery. This massive volume of data leads to more precise insights and improved performance in IP-related applications.

Why Digital Element is Unique

Digital Element’s ability to collect and analyze billions of IP observations is unique in the IP intelligence data space. This extensive dataset forms the backbone of all our products, and enables our customers to glean valuable insights about the traffic that accesses their networks.

Aggregating this data creates metadata lets us determine context such as:

  • Is this IP address coming from a public or private space?
  • Can I trust this IP address’s current geolocation? Based on if its dynamic or stable
  • Is this potentially a proxy IP address?
  • Does this IP address generally always belong to a given geographic region or is it geographically dynamic?
  • How much confidence can I have about its given location based on the number of observations at that location?
  • How much confidence can I have about its given location based on its last seen location?

Let’s see it in action.

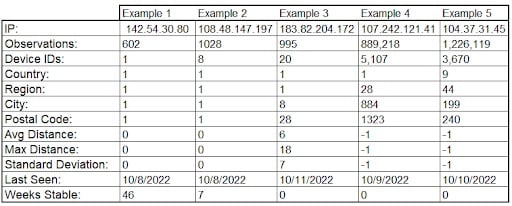
The above table shows five unique IP addresses. From the IP characteristics we can obtain nuanced context of each:

Key Takeaways: Example 1 is a stable IP address based on one geolocation observed over 600 times over 46 weeks. This IP address would likely be considered safe by all measures by a cybersecurity firm.

Key Takeaways: Example 2 is also a stable IP address even though it was only stable for 7 weeks. We see that there were over 8 devices from the same geolocation, making it likely it is a household with multiple computers and mobile devices.

Key Takeaways: Example 3 provides intelligence that this IP address is stable when considering the macro geographic location, but is unstable when looking at the city and postal code level, since it has over 20 devices connecting to it. Even though this IP address is considered unstable, it is likely safe due to the fact that the average and maximum distance between all the postal codes is small. This fact indicates that this IP address is likely a regional NAT. It is likely in a rural area where there are not enough IP addresses allocated there (unstable dynamic one).

Key Takeaways: Example 4 (mobile activity) and Example 5 (proxy activity) are clearly proxy IP addresses given the number of observations and devices connected to them being extremely high. However, the key difference is that Example 4 could be a corporate proxy IP address (relatively less malicious) given that it stays within the same country.

Key Takeaways: Example 5 has been seen in 9 countries. This IP address is clearly one that should be blocked when considering access to secure content.

IP Address Intelligence Experts Since 1999
Since our founding we have sought to provide context to anonymous traffic.

We started in the 1990s helping advertisers accurately and non-invasively target audiences based on their IP address. Since that beginning, we’ve been on a mission to provide as much IP address intelligence and data-driven context as possible to deliver even more value across many verticals.

Our product suite includes:

NetAcuityShines a spotlight on geography, delivering critical insights into location data
Nodify VPN CharacteristicsProvides unique context into VPNs, proxy networks and dark networks
Nodify IP CharacteristicsProvides deterministic data about an IP address:
  • Unique context you can’t find elsewhere
  • Enhances insight from NetAcuity and Nodify VPN for a fuller picture.


To learn more about our new IPC database, visit here.

What IP Address Stability Reveals About Your Audience

When Digital Element introduced its geotargeting technology in 1999, the most in-demand data point we gleaned from the IP address was a device’s geographic location. With the explosion of the Internet and ecommerce, numerous people, from digital marketers and advertisers, to cybersecurity professionals needed an accurate way to target messages based on location.

Over the decades, we introduced many new, non-geographic-based targeting parameters such as connection speed, domain name, language and ISP. This “IP Intelligence” encapsulated so much more than location, opening up new insights for organizations that they can use as a strategic advantage. IP stability is one of the highly strategic intelligence data points Digital Element can now offer clients.

Knowing the stability of an IP address can enhance numerous business use cases, such as protecting digital assets, enhancing digital analytics, and detecting and preventing online fraud.

What is IP Stability?

First let’s start with the basics: what is IP stability? The stability of an IP address refers to the period of time an IP address is observed in a specific geolocation. Some IP addresses are highly stable, meaning they’re associated with the same geolocation for months or years at a time. Others range in stability, as in stable to a given city for a given period of time, to  highly unstable mobile addresses that are associated with a different geolocation daily, or even hourly.

Types of IP Addresses

There are multiple types of IP addresses, which means there are also levels of IP stability. When speaking of IP stability, knowing the range of IP address type is essential. Let’s review:

Private IP addressThese are IP addresses that can only be used by devices (aka “hosts”) on the same network, such as a corporate network. These are non-Internet routable, and are clearly defined in RFC6761. The Request For Comment is the main standards setting body for the Internet.
Public IP address (aka internet routable addresses)These are IP addresses that are internet routable, meaning they can be reached from any device/machine in the world, and are clearly defined RFC1366, aka “Guidelines for Management of IP Space.” 
Fixed IP addressThese are IP addresses that are routed via cable, DSL or fiber infrastructure for internet connectivity, assigned to non-mobile devices. Fixed IP addresses can be both static and dynamic (see below).
Mobile IP addressThese are IP addresses that are routed via cell tower infrastructure for internet connectivity assigned to mobile devices. Mobile IP addresses are always dynamic IP addresses.
Static IP addressThese are IP addresses that have a consistent geolocation, meaning at the time it is analyzed, its geolocation is the same as previously identified. Static IP addresses are likely tied to the same building(s) if within an ISP block — i.e. the range of consecutive IP addresses that are grouped together for administrative or routing purposes.
Dynamic IP addressThese are addresses whose geolocations change frequently. They’re dynamic because they can service different end users at any given moment. Dynamic IP addresses are common in ISP, mobile carrier and proxy blocks because end users fluctuate within a given area. 

Naturally, we expect to see a higher degree of stability in the static IP presence, and low stability in both the dynamic and mobile presence. Therein lies many useful insights, as we’ll see below.

ISPs are the Decision Makers

Who decides if fixed locations will be assigned a static, rather than a dynamic, IP address? The answer is the ISPs themselves. Some ISPs will assign highly static IP addresses for their customers, while others opt to assign dynamic ones. 

For instance, Charter, an ISP that provides connectivity in the South, has very stable IP addresses, and some of its customers have had the same IP address for years. Across the pond, however, British Telecom will change the IP address of its residential customers on a daily basis. 

Mobile IP addresses have low stability. Digital Element has observed the same mobile IP addresses in dozens of locations over a brief period of time.

How Digital Element Assesses IP Stability

Digital Element’s IP Intelligence data can distinguish between static and dynamic IP addresses. We can also track the length of time a static IP address is tied to a specific geolocation, aka, its stability. We further break stability down into buckets of longevity:

Stability BucketNumber of Weeks Stable
No Stability0
Very Short Term1 – 4 weeks (1 month)
Short Term5 – 16 weeks (4 months)
Medium Term17 – 36 weeks (9 months)
Long Term37 – 52 weeks (12 months)
Very Long Term53 + weeks (more than 1 year)

Going further, Digital Element can look at the stability of IP addresses of each ISP within the fixed space (i.e. internet connectivity provided to residential homes or commercial spaces). This allows us to see their composition of static vs. dynamic. 

Finally, Digital Element tracks which ISPs have a high percentage of static IP addresses and which don’t. This, in turn, allows Digital Element clients to apply this insight for important business use cases, including eliminating waste in digital ad campaigns.

Digital Advertising and IP Stability

Storytelling is an important concept in digital advertising. Rather than target the same user with the same message over and over again, marketers want to display a progression of messages that take the user on a journey.

For instance, let’s say a user clicks on an auto manufacturer’s ad for a new car model. In this scenario, the user has shown an interest in the auto brand that the marketer will want to nurture by providing information about additional benefits, such as state-of-the-art safety features or fuel efficiency. To prompt the user along the journey the campaign will aim to target that same user with sequential messages.

Now let’s say the campaign fails to perform as expected, the brand manager may conclude that something was off with regards to the channels, creatives or messages chosen for the campaign. But is there another factor at play?

IP addresses are a standard method for targeting consumers within specific geographic regions. Optimum is an ISP that services the tri-state area of New York, New Jersey and Connecticut. As such, Optimum is responsible for assigning the IP address for its customers.

Here’s where things get tricky: Digital Element’s IP Intelligence data reveals a single IP address assigned by Optimum was seen from 109 devices across 44 cities and 59 postal codes. What’s more, the average distance between users was 27 miles. This is a fixed — not a mobile — IP address, meaning it is an IP address that is assigned to a residence or a commercial establishment.

Now, let’s say the marketer has targeted a storytelling campaign at IP addresses assigned by Optimum. The marketer will have no way of knowing if the same consumer saw any or all campaign messages, even though the campaign targeted fixed IP addresses.

If, however, that same campaign targeted IP addresses assigned by Charter to residential customers, the marketer can have a high degree of confidence that the same device was targeted for the sequential messaging campaign. 

IP Stability and Campaign Planning

IP Intelligence data allows marketers to apply a level of granularity to campaigns:

  • Target users with highly stable IP addresses with sequential messaging
  • Target users with less stable or dynamic IP addresses with more general campaign message

In short, IP stability insight helps marketers drive efficiency in media spend by suppressing sequential messaging for unstable or dynamic IP addresses. This is incredibly relevant, as media agencies tend to bid higher for impressions when they believe a user has been exposed to the initial messages in the sequence.

The stability of an IP address can also help marketers determine whether or not a specific user has visited a brand’s website. Let’s say a user clicks on an ad and visits the brand’s site. Now let’s say a device with the same IP address arrives on the site two months later.

If the stability of that IP address is short term or above, we can assume it’s a repeat visit — insight that can initiate a set of actions, such as offering an incentive to convert. If that IP address is dynamic and has very short term stability, it’s unlikely to be the same user who clicked on the ad or visited the website previously. 

Learn More

The availability of IP stability data allows digital marketers to make informed decisions in their campaigns, leveraging IP Intelligence’s granular data and vital context to reduce wastage, drive better outcomes, and ultimately deliver these benefits.

Want to learn more? Click here to get in touch.

Distinguishing Between Fixed and Mobile IP Addresses

The world of IP addresses is amazingly complex. This complexity stems from the fact that there are myriad types of IP addresses — private, public, fixed, mobile, static, dynamic — each of which are assigned a unique range.

In this blog post we’ll discuss two types of IP addresses: fixed and mobile IP addresses. We’ll cover what they are, how they differ, insights between the two of them, as well as how to tell one from the other. 

Let’s get into it.

A Quick Word on How IP Addresses are Assigned

IP addresses are just a string of numbers, which by themselves don’t tell you much. How they’re assigned — as well as to whom and for what purpose — is the source of Digital Element’s insights.

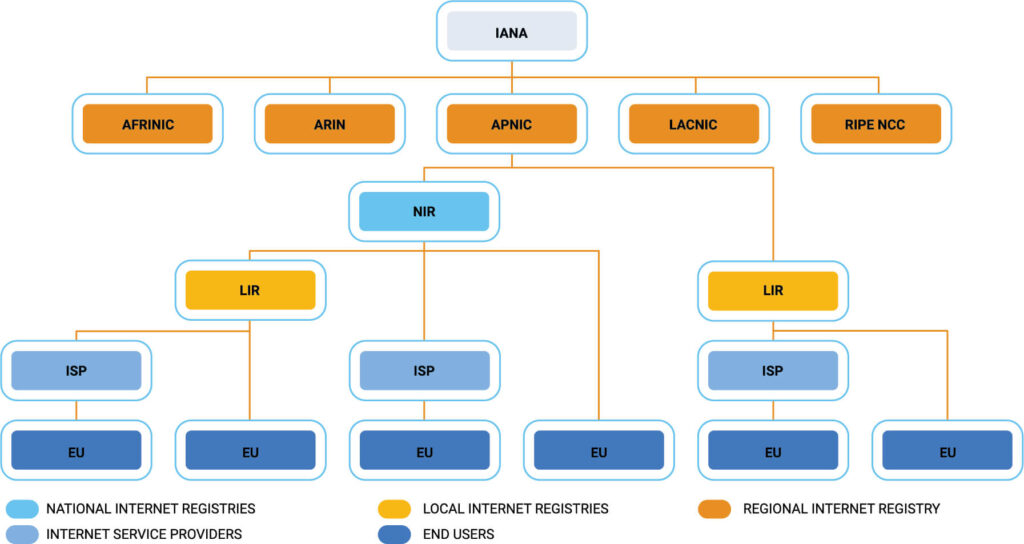
The process starts with the Internet Assigned Numbers Authority (IANA), an international governance body which is responsible for coordinating both the IP addressing systems across the globe, as well as the Autonomous System Numbers (ASNs) that are used for routing Internet traffic. An ASN is a unique identifier that is assigned to each network or a group of networks that are under common administrative control (e.g. an ISP located here in the U.S.). 

ASNs serve a crucial role in the operation of the Border Gateway Protocol (BGP). BGP is a routing protocol, and its purpose is to direct data (actually, data packets) between different autonomous systems in the most efficient manner possible. Naturally, those autonomous systems need unique IDs, ergo the ASN. The ASN itself includes a lot of data, including the organization to which it’s assigned and routing policies or the paths that data should take to reach it.

Back to assigning IP addresses … the IANA allocates pools of unallocated addresses to regional registries known as Regional Internet Registries (RIRs), according to their needs as described by Global Addressing Policies. 

The RIR then assigns the IP address blocks to a local Internet registry (LIR) or National Internet Registry (NIR), which then assigns them to an Internet Service Provider (ISP). Sometimes the RIR will assign a block of IPs directly to an ISP.

With the knowledge of which IP address blocks are assigned to which entities, powerful insights can be gleaned.  

What is a Fixed IP Address?

Fixed IP addresses are IP addresses that are routed via cable, DSL, or fiber infrastructure for internet connectivity and are assigned to non-mobile devices. Think: the home router or corporate network. Fixed IP addresses can be static or dynamic, it’s generally up to the ISP to make that decision.

  • Static IP addresses are those that have a consistent geolocation, meaning at the time Digital Element observes it, its geolocation is the same as previously identified. We track the degree to which static IP addresses are stable in weeks and months. Static IP addresses are likely tied to the same buildings within an ISP block.
  • Dynamic IP addresses are addresses whose geolocations change frequently. They’re dynamic because they can service different end users at any given moment. Dynamic IP addresses are common in ISP, mobile carrier and proxy blocks because end users fluctuate within a given area. 

What is a Mobile IP Address?

These IP addresses are typically assigned to mobile devices such as smartphones and tablets for internet connectivity that’s routed via cellular networks.

Mobile IP addresses are always dynamic, meaning they change frequently. When a mobile device connects to a cellular network, it is assigned an IP address from a pool of available addresses. This dynamic assignment allows cellular providers to efficiently manage their IP address resources.

Distinguishing Between Fixed and Mobile IP Addresses

Simply knowing the ISP that’s tied to an IP address itself can provide insight into the geolocation of the IP address, as well as whether it’s fixed or mobile. That means, of course, that we’ll need to understand a bit more about the ISP market.

There are four types of ISPs:

  1. Fixed ISP, such as Comcast and Charter. These ISPs provide internet connectivity to both homes and commercial entities. Some businesses, educational institutions and governments can act as their own fixed ISP. Some ISPs also provide WiFi hotspot connectivity.
  2. Mobile and fixed ISPs, such as AT&T. These ISPs provide connectivity to homes and businesses, as well as users on the go.
  3. Mobile-Only ISPs, such as Cricket Wireless. These ISPs provide connectivity for mobile devices only.
  4. Mobile connectivity for homes and businesses, such as T-Mobile and other 5G providers.

Again, knowing the blocks of IP addresses assigned to each type of ISP helps Digital Element to glean insights about the devices behind those addresses. For instance, we can look at an IP address and know that it is a fixed IP address that is highly stable and associated with a particular building in an office park. 

Why Distinguish Between Fixed and Mobile IP Addresses?

The ability to distinguish between the two types of IP addresses is very useful for businesses. Take, for instance, digital ad-tech companies that execute or measure mobile app install campaigns on behalf of agencies and app developers.

App install campaigns are rife with fraud. Nefarious players will attempt to pilfer the marketer’s budget by claiming installs that didn’t occur. The presence of a valid mobile IP in the data can help legitimate companies ascertain the validity of the install. Note: mobile IP alone will not be enough to validate app installs, but it provides critical context.

In other cases, a company, such as a brokerage, may only allow for on-premise access to sensitive information. Any request from a device with a mobile IP can be blocked automatically. That’s not to say that all mobile devices will be blocked; a user who is within the building can still access that data via a mobile phone. In this scenario, the user will sign in via the WiFi, and will have a fixed IP address, indicating that he or she is within the building.

Distinguishing between fixed and mobile IPs can also help drive efficiencies in knowing when to request additional authentication. Let’s say a consumer signs on to his bank from home every day in order to check his balance. The bank is likely to have a history of sign-ins from that fixed IP. Now let’s say that the consumer signs on from a mobile IP that is in a location far from his house. In this case, the bank may opt to require a second form of authentication.

IP address intelligence data alone won’t secure networks, but it can provide critical context to help businesses set smart rules to protect their — and their customers’ — data.

To learn more insights, download “The Definitive Guide to Understanding IP Addresses and VPNs and Implications for Businesses” or contact us to learn how IP geolocation can be leveraged in your industry. 

The Definitive Guide to Understanding IP Addresses and VPNs and Implications for Businesses

IP addresses sit at the foundation of nearly every digital business decision, yet they are also one of the most misunderstood components of the internet. As VPN usage, privacy relays, and anonymization services continue to grow, organizations are under increasing pressure to understand what an IP address really represents, how trustworthy it is, and what risks or opportunities it introduces by use case.

For security teams, this may mean distinguishing a benign corporate VPN from a risky anonymizer. For media, ecommerce, and compliance teams, it can mean determining whether traffic is coming from a legitimate user, a privacy relay, or a commercial VPN endpoint that could undermine licensing, fraud prevention, or regional enforcement.

To help businesses navigate this complexity, Digital Element created The Definitive Guide to Understanding IP Addresses and VPNs and Implications for Businesses, a comprehensive white paper designed to establish a practical, business-ready understanding of IP address intelligence and IP geolocation.

Why Understanding IP Addresses & VPNs Matters for Business

Most people are familiar with IP addresses and the role they play in connecting devices to networks. Many organizations already rely on IP address intelligence to support day-to-day operations, whether that’s targeted advertising, cybersecurity enforcement, fraud prevention, or compliance with global licensing and regulatory requirements.

What’s far less understood is how different types of IP addresses behave, how VPNs and privacy technologies complicate attribution, and how to interpret IP signals accurately without overblocking or introducing unnecessary risk.

That’s exactly why subject matter experts across Digital Element collaborated to develop an authoritative resource that demystifies the IP address space and explains how businesses can apply IP intelligence responsibly and effectively.

What This White Paper Helps You Understand

The Digital Element white paper starts at the very beginning, in the origins of the internet, and builds toward modern challenges facing enterprises today. Along the way, it explains:

  • How IP addresses are created, assigned, and managed globally
  • The differences between IP address types and accuracy levels
  • How VPNs, proxies, and privacy relays affect IP-based decisioning
  • Where IP geolocation data is reliable and where it has limitations
  • What signals separate privacy relays from commercial VPN endpoints?
  • How can we differentiate legitimate corporate VPN usage from risky anonymizers?
  • Can IP intelligence support enforcement without harming user experience?

Chapter Breakdown: What You’ll Learn

Chapter 1: Introduction to IP Addresses

This chapter explores the origins of IP addresses, why they were created, and how they evolved alongside the internet. It defines the many types of IP addresses in use today and clarifies commonly misunderstood concepts such as the differences between static, fixed, and dynamic IPs.


Chapter 2: The Evolution of IP Geolocation Data

Here, the paper examines how IP geolocation developed and how IP address allocation changed as the internet scaled globally. It explains the impact of IoT growth, IPv4 exhaustion, and the introduction of IPv6, along with critical technologies like NAT and CGNAT that affect address stability and interpretation.


Chapter 3: IP Geolocation Reliability and Vulnerabilities

This chapter looks closely at the strengths and limitations of IP geolocation data. It explores where inaccuracies and vulnerabilities arise, and how Digital Element addresses these challenges through continuous data refinement and contextual intelligence.


Chapter 4: How IP Addresses Are Allocated

Readers gain insight into how IP blocks are assigned to ISPs and enterprises worldwide, why allocation strategies differ, and how these decisions influence IP stability. The chapter also explains how Digital Element leverages allocation knowledge to add meaningful context to IP address intelligence.


Chapter 5: The VPN and Proxy Landscape

As VPN adoption accelerates, this chapter provides a clear breakdown of proxies, VPNs, darknets, and residential IP services. It explains why security and compliance teams need to differentiate between benign corporate VPN traffic and high-risk anonymization services, and how IP intelligence contributes to that assessment.


Chapter 6: Parting Thoughts and Emerging Trends

The final chapter highlights key trends shaping the future of IP geolocation, including 5G adoption, IPv6 expansion, IoT growth, and the continued rise of VPN and privacy technologies.

Why Download the Digital Element IP Geolocation White Paper

Whether you’re responsible for cybersecurity, fraud prevention, advertising performance, or regulatory compliance, understanding IP addresses and VPN behavior is no longer optional.

This white paper equips you with the knowledge needed to:

  • Evaluate IP-based risk more accurately
  • Understand how VPNs and privacy relays affect IP signals
  • Make informed decisions without overblocking legitimate users
  • Apply IP geolocation responsibly across business use cases

If you have questions about IP intelligence, VPN detection, or how Digital Element supports enterprise use cases, contact our team, we’re happy to help.

Download the Guide Now

Five Ways IP Intelligence Data Helps Broadcasters

Broadcasters serve a vital role in communities across the country. In addition to providing news and information to communities, broadcasters are instrumental to the economy. Per the National Association of Broadcasters (NAB), local broadcasting supports 2.46 million jobs in the U.S. and contributes $1.19 trillion to the nation’s GDP.

Given the economic and societal importance of broadcasters, it is vital for them to have accurate data to ensure they deliver the right content, personalize the user experience, and protect the digital rights of content owners. Digital Element’s NetAcuity and Nodify give broadcasters accurate, global IP intelligence data to help solve some of these challenges.

In short, IP geolocation and intelligence tools help broadcasters:

  1. Support licensing and copyright compliance by restricting content based on precise geographic location
  2. Serve and personalize ads to the right audience at the right place and time
  3. Enhance the user experience by optimizing content delivery for each viewer’s connection and device
  4. Fight piracy by detecting VPNs, proxies, and residential proxy networks used to access out-of-market content
  5. Strengthen cybersecurity by distinguishing real residential IP addresses from proxied ones

Let’s look at some of the most important use cases.

#1: Licensing & Copyrights Compliance

Copyright owners never give licensors carte blanche with their intellectual properties. The more people who see or use their audio or video content, the more royalties they earn. Those agreements are negotiated by region.

Digital Element’s NetAcuity helps broadcasters support compliance with licensing and copyright agreements. Programming content is served to audiences based on country, state/region, city, and ZIP/postal code, enabling broadcasters to restrict access to their digital assets in prohibited or embargoed areas. Nodify adds to this by identifying users hiding behind proxies to get around location restrictions, helping broadcasters further protect rights holders.

#2: Ad Serving & Content Personalization

Every marketer is keen to display the appropriate content to the right user in order to increase engagement and, ultimately, ROI.

For example, by targeting postal codes near a tentpole event, such as a music festival or a major sporting event, marketers can deliver just-in-time ads to receptive audiences (think: transportation ads to the big event, or ads that drive traffic to a local eatery franchise). Ads that reach consumers at the right place and the right time deliver higher engagement and ROI.

NetAcuity is privacy-conscious, enabling marketers to tap into a wide variety of contextual data so that they can deliver relevant content to the right audiences. Additional insights, including demographic data, allow brands to target ads relating to a population in an area or region.

#3: Enhanced User Experience

Content delivery networks (CDNs) help ensure a positive user experience by delivering content at the optimal speed based on connection, or in the ideal format based on the viewer’s device. They also process incoming requests and deliver content to any point on the network on demand, while managing entitlements and access to video assets based on the authentication of user rights and integration into the order process.

Digital Element’s NetAcuity automatically detects the connection type and speed of the device, helping the CDN to ensure content is delivered at the right speed and format for the device, providing customers with high-quality viewing and sound quality with no delays or buffering interruptions.

#4: Fighting Piracy

Piracy is a scourge that threatens the broadcasting sector, putting protected content, revenue, and even jobs at risk. In its 2021 report, the Motion Picture Association (MPA) estimates that online TV and film piracy costs the U.S. economy a minimum of  $29 billion in lost revenue each year, and robs the industry of hundreds of thousands of jobs.

Much of that piracy stems from consumers accessing content that’s outside of their markets, which they can easily do with any of the many VPNs available. In their defense, leveraging VPN to access out-of-market content is so widespread and common that many consumers may not be aware it typically violates the service’s terms of use and the licensing agreements behind the content.

Digital Element’s director of product management discusses piracy at NAB 2022

Digital Element’s Nodify can determine whether inbound traffic is tied to a VPN, proxy, or a darknet, enabling broadcasters to block proxy and darknet traffic proactively, or prompt users for additional authentication (an important consideration as many people use VPNs for privacy or for work, and a global ban of VPN traffic will penalize many legitimate users).

Content pirates are switching tactics, switching from VPNs to residential IP proxy networks to circumvent detection. These are networks that pay consumers to share their internet across devices, and then enable other customers to “rent” that consumer traffic. However, Nodify can detect residential IP proxies, enabling broadcasters to block such traffic.

#5: Enhance Cybersecurity

Web Application Firewalls (WAFs) are important tools for broadcasters, but the rise of residential IP proxy networks has given nefarious actors a workaround. WAFs look at the IP address and geo-location of devices seeking to access a broadcaster’s web applications, and if they are residential and located within the right city or region, grant access. But without additional contextual data around network traffic, like that provided by Nodify, WAFs cannot distinguish between residential IP addresses that are real and those that are proxied.

We advise our clients that protecting their web applications requires a strong cybersecurity posture, especially considering the rise in VPN usage. Layering in threat intelligence insights, such as VPN intelligence data, can help protect your geo-filtering ecosystem; these insights allow streaming media companies to protect revenue by determining which connections pose risks and prevent bad actors from circumvention activities by identifying anonymized connections or connections from certain geographies. When an incident does slip through, IP Forensics gives security teams the historical look back necessary to trace how a compromised or proxied connection behaved over time, helping broadcasters investigate breaches and strengthen defenses after detection.

Getting Started with IP Intelligence for Broadcasters

Accurate IP geolocation and intelligence data touches nearly every part of a broadcaster’s digital operation, from what content can legally be shown where, to how ads are targeted, to how piracy and cyber threats are kept at bay.

As VPN usage and residential proxy networks continue to grow, having reliable, contextual IP data isn’t just a nice-to-have; it’s foundational to protecting revenue, rights holders, and viewers alike.

Talk to a Digital Element specialist today to find the right solution for your broadcasting needs.

Frequently Asked Questions About IP Geolocation and Intelligence Tools

How quickly can a broadcaster integrate IP intelligence data into existing systems?

Most broadcasters can integrate IP intelligence data through APIs or database downloads within a matter of days to a few weeks, depending on the complexity of existing infrastructure (CDNs, ad servers, WAFs, etc.) and how many systems the data needs to feed.

What’s the difference between NetAcuity and Nodify, and when would a broadcaster use each?

NetAcuity, Digital Element’s core IP geolocation database, is used to determine the location of a device down to the country, region, city, or ZIP/postal code. This is the foundation for content licensing, geo-restriction, and ad targeting. Nodify, on the other hand, focuses on threat and proxy intelligence — detecting VPNs, proxies, darknets, and residential IP proxy networks. Broadcasters typically use NetAcuity to determine where a viewer is located, and Nodify to verify whether that location can be trusted, making the two complementary rather than interchangeable.

What should broadcasters look for when choosing an IP intelligence data provider?

Key factors include geolocation accuracy and granularity (country vs. city vs. ZIP/postal code), VPN and proxy detection rates, update frequency, ease of integration, and a provider’s track record with content licensing and rights holder compliance use cases specifically. Requesting a trial or proof of concept against real traffic data is the most reliable way to verify a provider’s accuracy claims before committing.

Do broadcasters need to block all VPN traffic to protect licensed content?

No. Many viewers use VPNs for legitimate reasons, such as privacy or remote work, so blanket VPN blocking can unnecessarily penalize legitimate users. Instead, broadcasters can use contextual data, like that provided by Nodify, to distinguish between VPN traffic tied to legitimate use and traffic associated with piracy or policy circumvention, then apply proportionate responses such as additional authentication rather than an outright block.